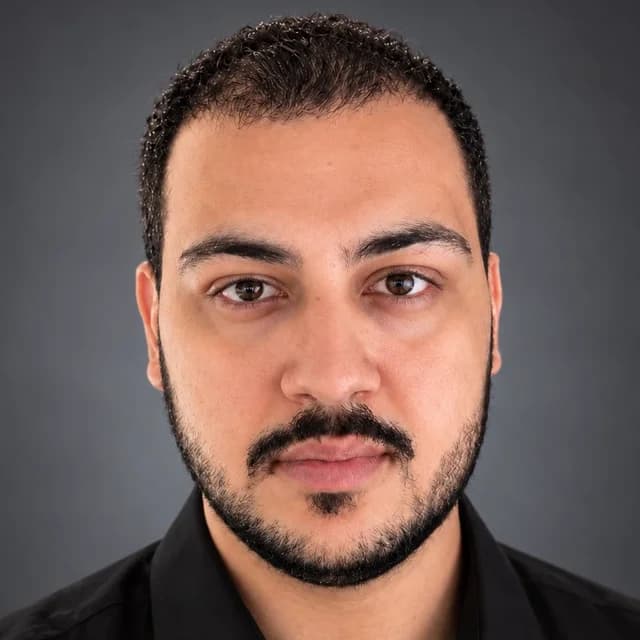
Thomas
Ibrahim
Embedded Systems EngineerFirmware & IoT Security
I talk to microcontrollers more than most people. They're better listeners.
Available immediatelyAuthorised to work in FranceValence, France
- CPUFirmwareFreeRTOS tasks and bare-metal C on ESP32 and STM32
- PLProgrammable logicRSA and AES cores in VHDL, on Basys-3 and Zybo-Z7
- I²CSensor driversMAX30102, BMP280 and DS18B20 over I²C and 1-Wire
- SECCryptoPer-device HMAC-SHA256 and a durable replay guard
- RFRadioBLE GATT at 1 Hz, MQTT 5 over TLS
- VDDPower pinDPA and EM side-channel analysis
SecureVitalsa secure IoT health-monitoring fleet
Featured case study
Embedded systems & IoT security internship, Jelecom · 2026
The problem
Health sensors spread across a fleet of devices produce data that has to be trusted. A tampered or replayed reading, or one node impersonating another, puts false values in front of whoever relies on them. The goal: remotely programmable nodes streaming vital signs in real time, with every message authenticated from the device to the dashboard.
Results
| Parameter | Value |
|---|---|
| nodes streaming concurrently at 1 Hz | 4 |
| automated tests across firmware, ingestion, web and mobile | 202 |
| frozen, versioned wire-format contracts | 3 |
Architecture
Security design
Per-device HMAC-SHA256
Every payload is signed with its node's own key over a canonical field ordering, so the backend can prove which device sent it and that nothing changed in transit.
Constant-time verification
Signatures are compared in constant time, so response timing gives an attacker nothing to work with when forging a tag.
Durable replay guard
Replayed messages are rejected, and the guard's state survives backend restarts, so a restart never reopens the replay window.
From a global key to per-device keys
The first design shared one secret, which let any node impersonate another. Migrated to per-device key resolution, with duplicate keys rejected at configuration time.
STRIDE threat model
Threats and mitigations documented with STRIDE and mapped to IEC 62443 and GDPR Article 32.
Projects
SecureVitals: Secure IoT Health Monitoring Platform
ESP32 / Python / Next.js / React NativeFeatured
Four-node IoT health-monitoring fleet streaming signed sensor telemetry (SpO2, heart rate, pressure, temperature) at 1 Hz. End-to-end stack: FreeRTOS firmware with custom sensor drivers and BLE GATT, MQTT 5 over TLS with per-device HMAC authentication and replay protection, a Python ingestion service, a Next.js dashboard and a React Native iOS app, covered by 202 automated tests.
Read the case study- ESP32
- FreeRTOS
- BLE
- MQTT
- TLS
- HMAC-SHA256
- IoT security
- Next.js
- React Native
Hardware Implementation of Modular Arithmetic for RSA
Basys-3 FPGAFeatured
Implemented modular addition, multiplication and MSB-first exponentiation in VHDL, verified with self-checking testbenches, and synthesized a complete 16-bit RSA encryption/decryption core. Demonstrated a hardware brute-force attack on a small RSA key space.
- FPGA
- VHDL
- cryptography
- RTL
- verification
- security
Line-Following Robot
Arduino Uno
Autonomous robot using IR sensors and a tuned PID motor-control loop with PWM driving for stable tracking on curved paths.
- Arduino
- PID
- real-time
- control
Water Level Controller over UART
Arduino Uno
Two-node system: a keyboard-driven master sends level setpoints over a custom UART protocol to a slave controlling a pump and valve, with interrupt-driven I/O and closed-loop level control.
- Arduino
- UART
- embedded
- control
Side-Channel Attack Labs: DPA & EM Analysis
Embedded microcontrollers
Differential Power Analysis and electromagnetic leakage experiments on embedded microcontrollers, with automated oscilloscope acquisition pipelines and evaluation of hardware countermeasures.
- DPA
- EM analysis
- side-channel
- fault injection
- security
Arbiter RTL Verification and Fault Injection
VHDL / ModelSim
Priority arbiter in VHDL with a complete verification environment: protocol checker, property checker, randomised driver with file I/O and PSL assertions. Performed SEU fault injection and implemented a hardware countermeasure, reaching full functional coverage of the arbitration logic.
- VHDL
- RTL
- verification
- PSL
- fault injection
- SEU
AES Hardware Implementation with I2C Temperature Sensor
Zybo-Z7 FPGA
Full AES encryption pipeline in VHDL (SubBytes, ShiftRows, MixColumns, AddRoundKey, key scheduling) on a Zybo-Z7, encrypting live data from an I2C temperature sensor. All pipeline stages verified in hardware.
- FPGA
- VHDL
- AES
- cryptography
- I2C
- Zynq
ARM NEON SIMD Performance Analysis
Zynq-7020 SoC (Zybo Z7-20)
Benchmarked scalar vs. NEON SIMD kernels at 667 MHz using CPU cycle counters: 2.05x (array sum), 1.46x (4x4 matrix multiply) and 2.51x (edge detection) speedups. GCC -O3 gave a 10x improvement over unoptimised scalar code.
- SoC
- ARM
- NEON
- SIMD
- performance
- C
FPGA-Based Falcon Post-Quantum Signatures with AES
FPGA
Implemented the Falcon lattice-based post-quantum signature scheme alongside AES encryption in a single FPGA design.
- FPGA
- post-quantum cryptography
- Falcon
- AES
- security
UART Co-Verification
RTL / ModelSim
UART module verified by co-verification against a software reference model, covering frame structure, baud-rate timing, parity checking and error handling with directed and random test vectors.
- UART
- RTL
- verification
- testbench
AI Cryptanalysis of Lightweight Block Ciphers
Python / ML
Analysed the security of S-AES and S-SPECK using AI-driven cryptanalysis and demonstrated exploitable weaknesses in reduced-round variants.
- cryptanalysis
- AI
- machine learning
- research
Experience
02/2026 – 09/2026Embedded Systems & IoT Security InternJelecom
- Designed and brought into service SecureVitals, a fleet of four remotely programmable IoT health-monitoring nodes streaming concurrently at 1 Hz through a single signed telemetry path, building the full stack: ESP32 firmware, a Python ingestion service, a Next.js operations dashboard and a React Native (Expo) iOS app.
- Developed the ESP32 firmware in C++ with FreeRTOS tasking, MAX30102 (SpO2/heart rate), BMP280 (pressure) and DS18B20 (temperature) drivers over I2C and 1-Wire, and a BLE GATT service notifying at 1 Hz within a 180-byte payload budget; took the design from breadboard prototype to a repeatable build-and-flash workflow across all four units.
- Secured the device-to-cloud boundary with MQTT 5 over verified TLS, per-device HMAC-SHA256 over a canonical field ordering, constant-time verification and a durable replay guard that survives backend restarts, so tampered or replayed payloads never reach application state.
- Eliminated a shared-secret weakness that let any node impersonate another by migrating from a single global key to per-device key resolution with configuration-time duplicate-key rejection.
- Made the platform maintainable by a team: 202 automated tests across firmware, ingestion, web and mobile suites under Git and continuous integration, three frozen versioned wire-format contracts, and documentation including a STRIDE threat model mapped to GDPR Article 32 and IEC 62443.
12/2024 – 08/2025Full-Stack Developer (Freelance)Veeyra AI – Private Clinic
- Sole developer: delivered a complete patient management system into day-to-day production use at a live medical clinic over 8 months, owning requirements gathering with the end users, deployment, commissioning and handover documentation.
- Built a FastAPI back end with JWT authentication, role-based access control and PostgreSQL, supporting concurrent multi-role access to a shared clinical dataset, with a React.js front end covering patient records, financial dashboards and automated receipt generation.
- Integrated an AI chat assistant that answers natural-language questions over patient data using the Anthropic API.
05/2024 – 12/2024Penetration Testing InternDEPI
- Delivered black-box and grey-box penetration tests on web applications and internal network infrastructure, and produced structured vulnerability reports with reproduction steps, severity ratings and remediation recommendations.
- Reduced manual reconnaissance and scanning effort by automating both phases in Python on GNU/Linux, on top of Nmap, Metasploit and Burp Suite.
08/2023 – 09/2023Integration Engineer InternNational Bank of Egypt
- Deployed two BizTalk Server load balancers to manage message routing between database servers.
- Configured orchestration pipelines, monitored message flow across backend services, and documented root causes of integration failures for the infrastructure team.
06/2022 – 07/2022Penetration Testing TraineeTelecom Egypt
- Assisted the security team with manual testing of internal web portals and network services.
- Wrote Python scripts to automate header analysis and port enumeration, reducing manual testing time.
Skills
- Embedded & RTOS
- ESP32
- STM32
- FreeRTOS
- bare-metal C
- interrupt-driven I/O
- sensor drivers
- PlatformIO
- Arduino
- Raspberry Pi
- Protocols
- I2C
- UART
- SPI
- 1-Wire
- BLE GATT
- MQTT 5
- TLS 1.3
- HMAC-SHA256
- Security
- Secure Boot
- Cryptography
- mbedTLS
- DPA
- EM analysis
- fault injection
- STRIDE
- IEC 62443
- GDPR Art. 32
- penetration testing
- HDL & FPGA
- VHDL
- Verilog
- SystemC
- Vivado
- Vitis
- ModelSim/Questa
- Xilinx Basys-3
- Zybo-Z7
- Zynq SoC
- Programming languages
- C
- C++
- Python
- TypeScript
- VHDL
- Verilog
- Tools
- Git
- CI
- GNU/Linux
- Oscilloscope
- Nmap
- Metasploit
- Burp Suite
- Methodologies
- Hardware/software co-design
- RTL verification
- PSL assertions
- Testbench development
- Threat modelling
Education & languages
Education
08/2025 – 09/2026
MSc, Embedded Systems Security (International Master)
Grenoble INP – Esisar, Valence, France
- Design & Verification of Embedded Systems
- Embedded Systems Security Labs
- Hardware Security Labs
2019 – 2024
BSc, Computer Engineering
British University in Egypt (BUE)
- Research project: AI-driven cryptanalysis of lightweight block ciphers (S-AES, S-Speck), graded A+
Languages
- Arabic
- Native
- English
- Fluent
- French
- Intermediate (B1)
Contact
Hiring for an embedded, firmware or IoT security role? I'd be glad to talk.
thomas.e.ibrahim@gmail.com